Overview
This is Mountain View High School’s (team mv-infosec) design for the 2026 MITRE eCTF competition, building on MITRE’s insecure reference design for a Hardware Security Module (HSM). The HSM supports secure file storage and transfer between devices.
Features
- List Files: list metadata of all files stored on the HSM
- Read File: read a specified file’s name and contents
- Write File: write data to a specified slot on the HSM
- Listen mode: put the device into a state where it can communicate with other HSMs
- Interrogate Files: request the file list from an adjacent HSM
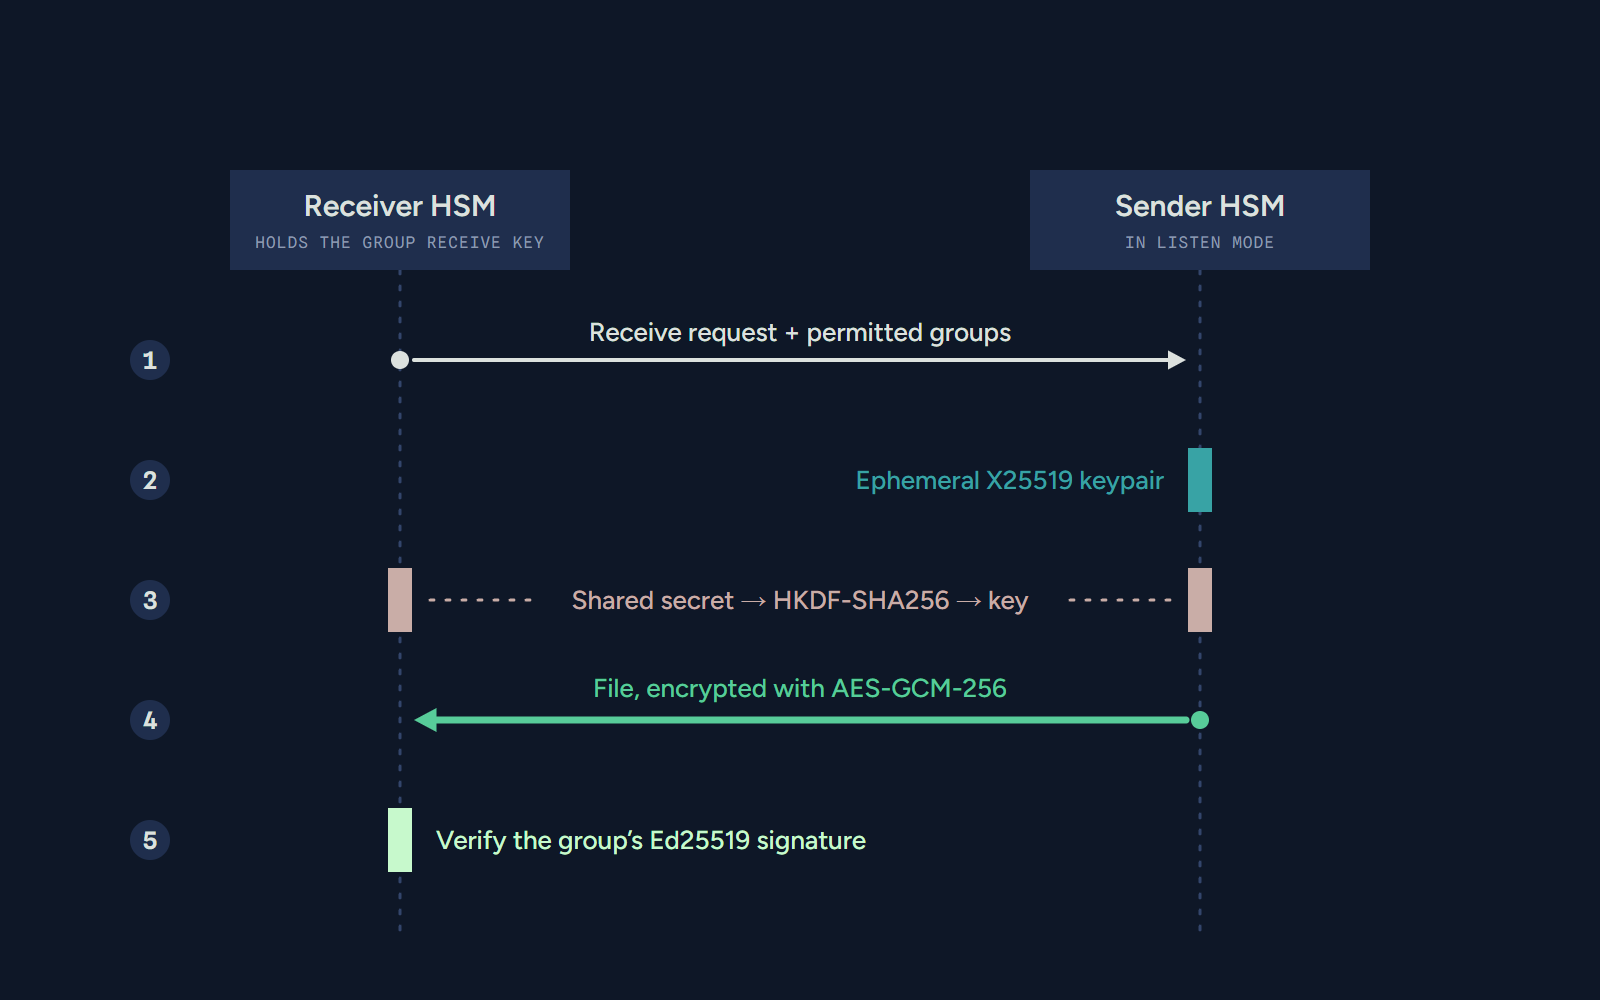
- Receive File: request a file from an adjacent HSM
How it works
The reference design’s firmware is C targeting an MSPM0L2228 microcontroller, built via a Makefile and Docker-based build environment supplied by the eCTF organizers. The team is additionally developing a Rust-based firmware implementation (crate lebron) using the Embassy async embedded framework, with its own Dockerfile and Cargo-based build. A separate pip-installable Python module (ectf26_design) generates the shared secrets used to provision HSMs.
Contribution
- Wrote the team design document in LaTeX (
docs/design-doc.tex), including the cryptography, protocol and security-requirement sections in the first design doc submission - Set up the Rust firmware build: Cargo configuration, Embassy and Cortex-M dependencies, and the
memory.xlinker memory layout - Added the Dockerfile and build script for the Rust firmware